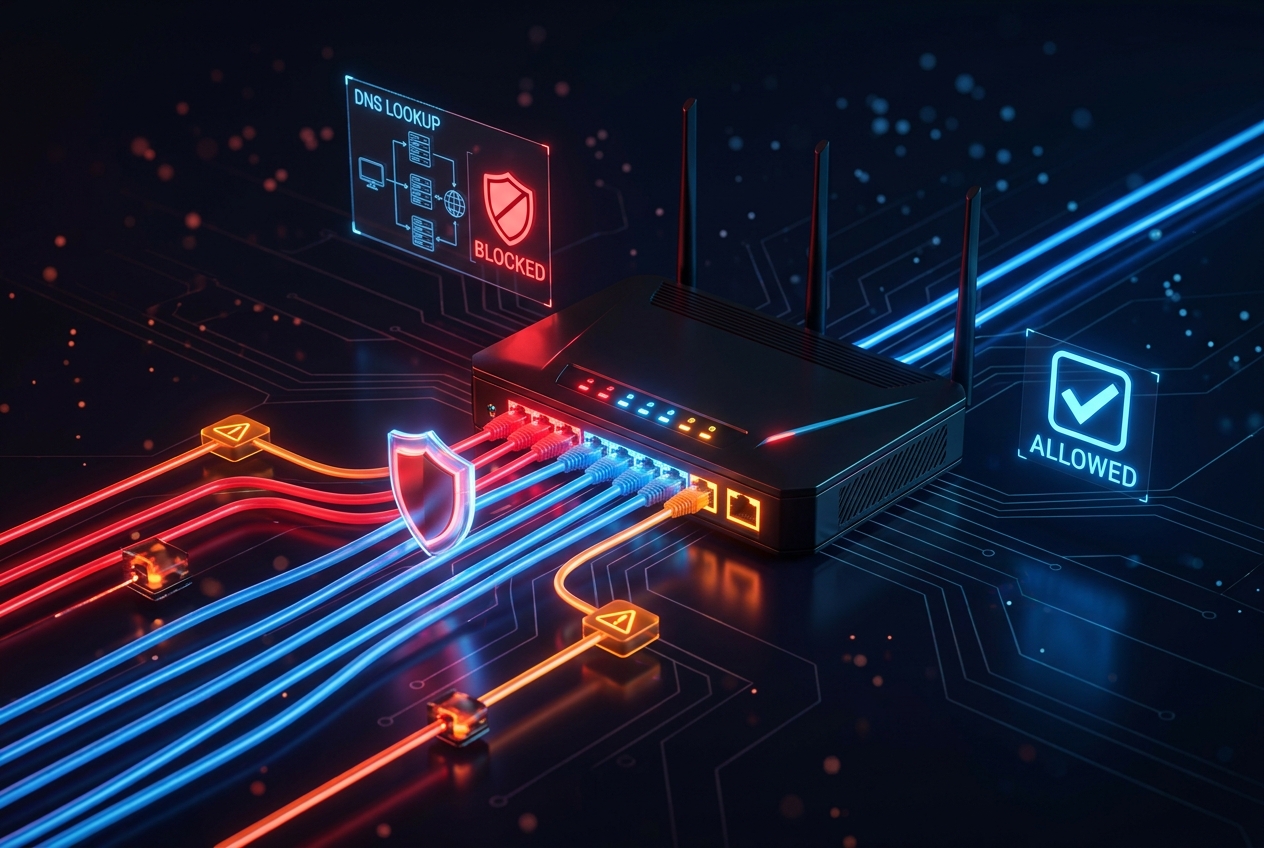
DNS Security: Filtering and Blocking Malicious Domains on the Router
Your router sees every DNS query on the network — which makes it the perfect place to block malware, phishing, and command-and-control domains before a device ever connects to them.
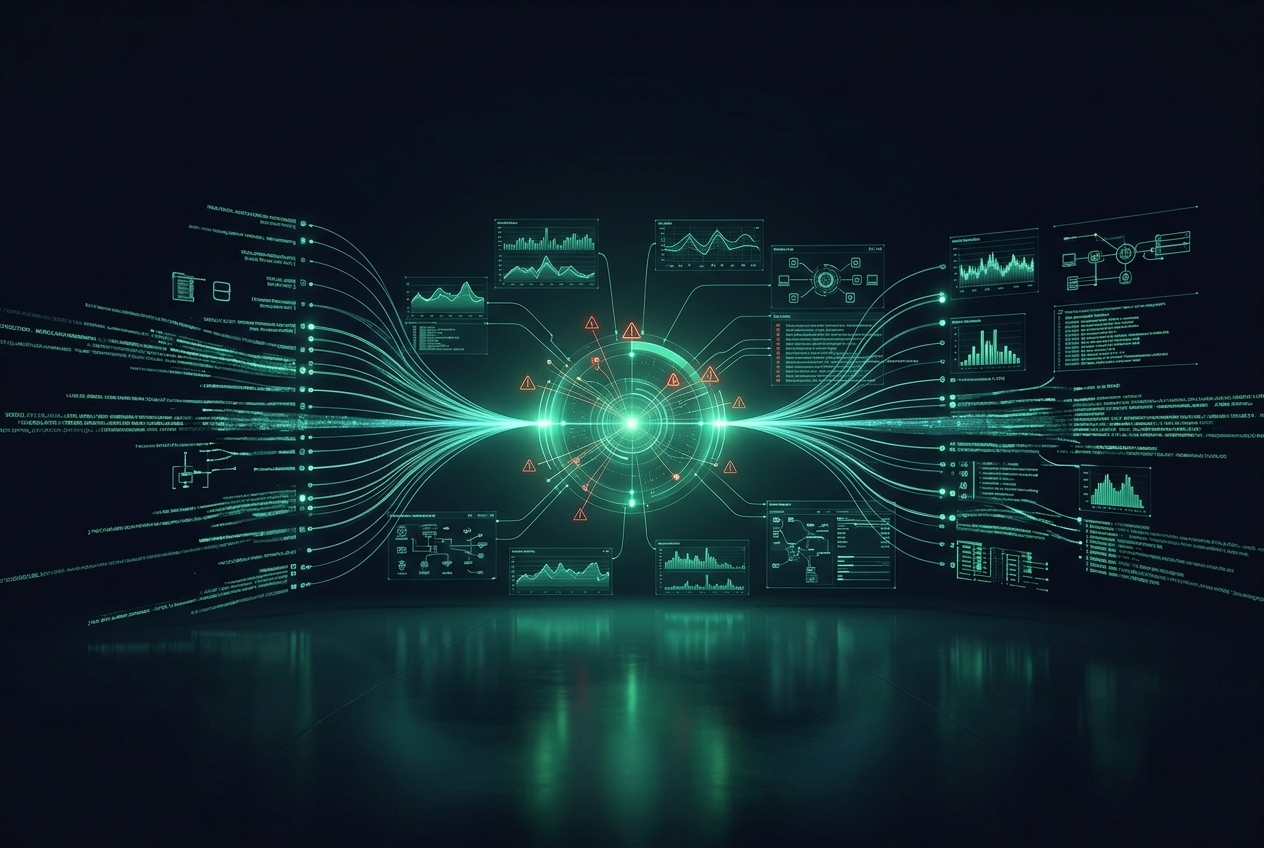
How SIEM Works: Turning Log Noise into Security Signal
A SIEM collects logs from everywhere, correlates them, and surfaces the handful that actually matter. Here's how the pipeline works and how to get real value from it.
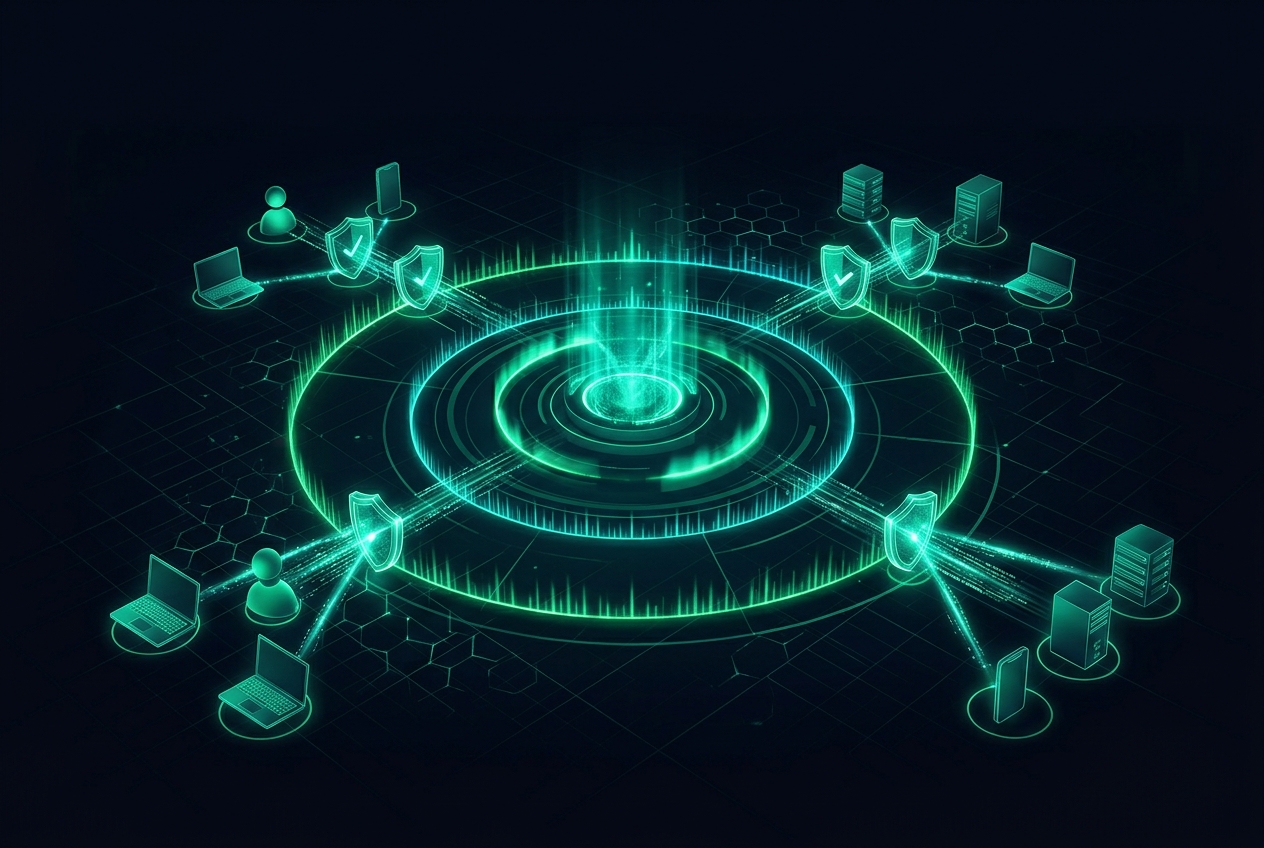
Zero Trust Explained: Never Trust, Always Verify
The old castle-and-moat model is dead. Here's how Zero Trust works, its core principles, and a practical path to adopting it without boiling the ocean.
VPNs Explained: How the Encrypted Tunnel Works — and Its Real Pros & Cons
What actually happens to your traffic the moment you hit “Connect”? A plain-English look inside the encrypted VPN tunnel — how it hides your data and IP, what it quietly can't protect, and the real pros and cons before you trust one.
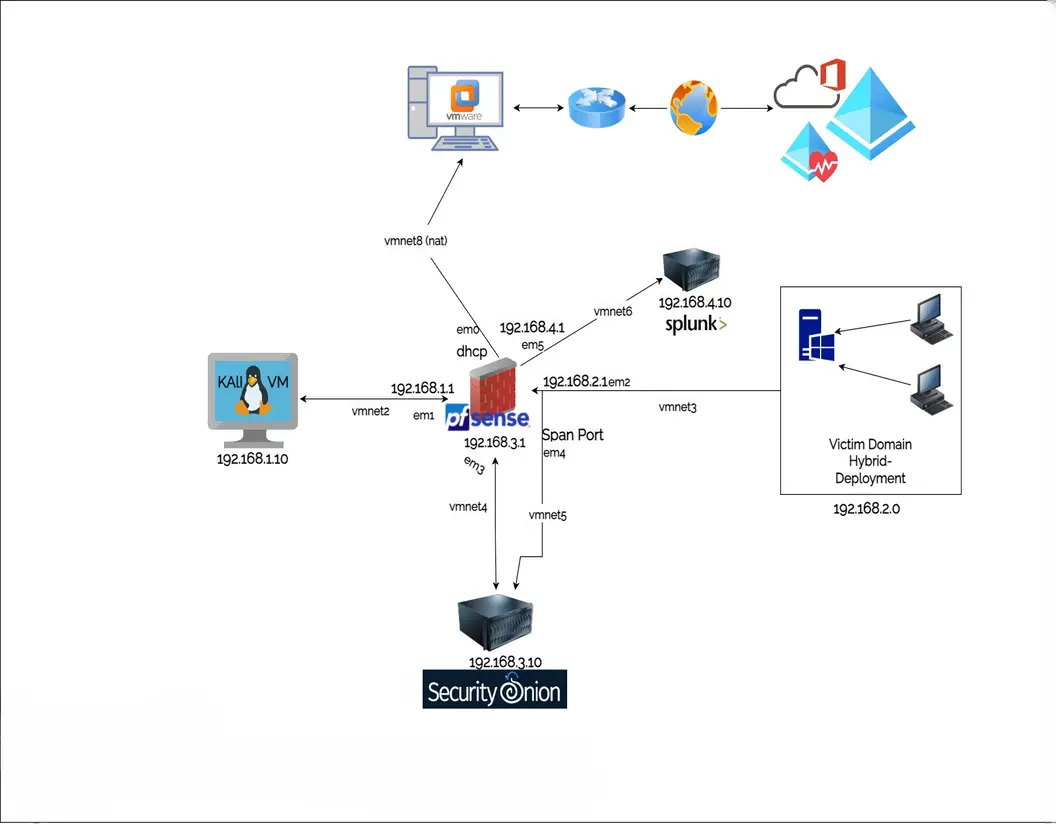
Cybersecurity Lab: Network Traffic Detection and Analysis
Attacks hide inside ordinary-looking traffic. In this home-lab build I capture live packets, feed them through an IDS, and hunt for the tell-tale signals of an intrusion — scans, beacons, exfil — turning raw PCAPs into detections you can actually act on.
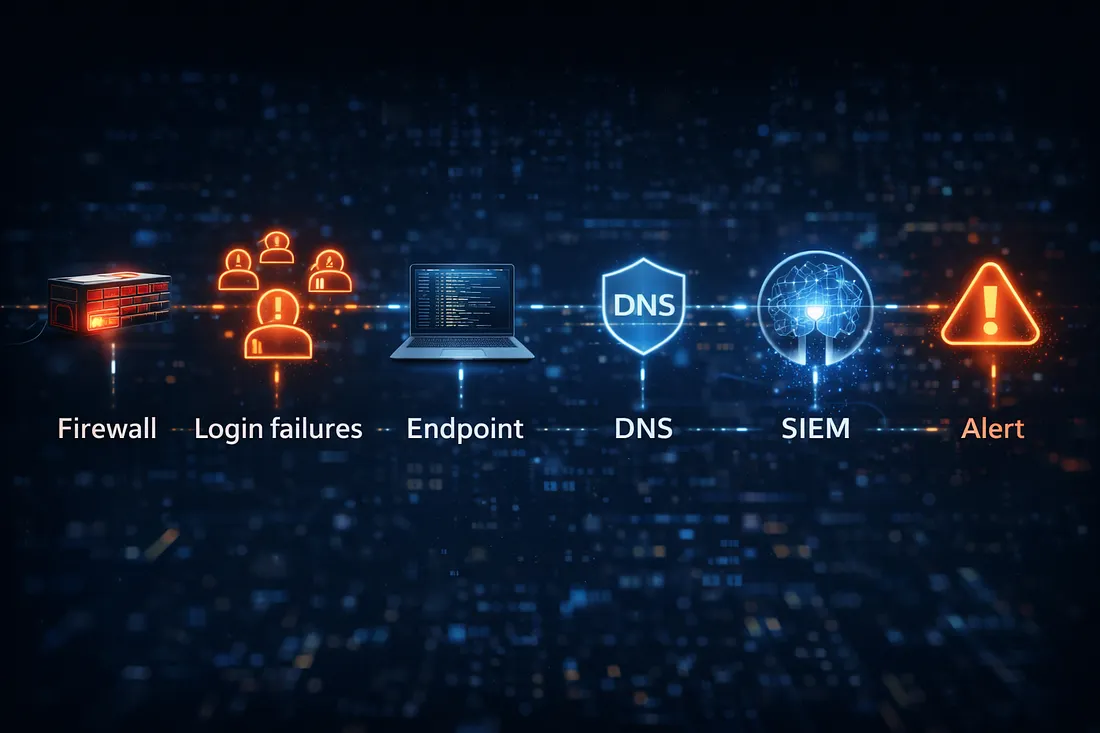
From Logs to Alerts: Getting Started with SIEM
How a Security Information and Event Management platform turns raw noise into actionable detections — and how to start with Splunk.

Building a Cybersecurity Home Lab from Scratch
Everything you need to spin up a safe, isolated lab for practicing detection, incident response, and offensive techniques.
Building an Incident Response Playbook That Actually Works
A playbook you only write after an incident is a post-mortem. Here is how to build one before the alarm goes off — so your team acts calmly instead of scrambling.
Phishing Defense: Spotting and Stopping Social Engineering
Attackers target people, not just systems. Learn the tells of a phishing attempt and the habits that stop them cold.